Which standards guide security optimization for access control?
The most useful security optimization standards combine access control requirements, cybersecurity safeguards, interoperability specifications, and local life safety rules. No single standard covers every evaluation need.
For technical evaluators, IEC 60839-11-1 provides a starting point for electronic access control requirements. Other frameworks address installation, credential protection, operational governance, and emergency behavior.
The practical task is selecting applicable requirements and translating them into acceptance tests. A compliance claim alone cannot establish whether an installed system protects a particular facility.
GSIM approaches this evaluation by connecting standards with procurement evidence, integration testing, and operational assurance. The objective is measurable protection aligned with site risks and legal obligations.
Which standards belong in an access control evaluation?
Start with the facility’s jurisdiction, occupancy, threat profile, and system architecture. These factors determine which requirements are mandatory, contractually binding, or useful as evaluation guidance.
The following standards and frameworks address different evaluation layers. Check their current editions, regional adoption, and contractual applicability before incorporating specific clauses into procurement documents.
These references are complementary. Product testing, organizational certification, communication protocols, and building regulations answer different questions and should remain distinct within an evaluation report and procurement specification.
What does IEC 60839 establish—and what must you verify separately?
IEC 60839-11-1 addresses requirements for electronic access control systems and components. Use it to structure questions about system functionality, security performance, and relevant environmental conditions.
Request evidence identifying the exact equipment, software versions, configurations, and classifications assessed. A supplier’s general statement of conformity provides insufficient detail for a defensible technical decision.
IEC 60839-11-2 supports application planning, installation, operation, and maintenance. It helps evaluators examine whether deployment practices preserve the protection intended by the system design and requirements.
Translate applicable requirements into site scenarios: unauthorized entry attempts, door tampering, forced openings, communication faults, and power interruption. Specify the expected response for each scenario.
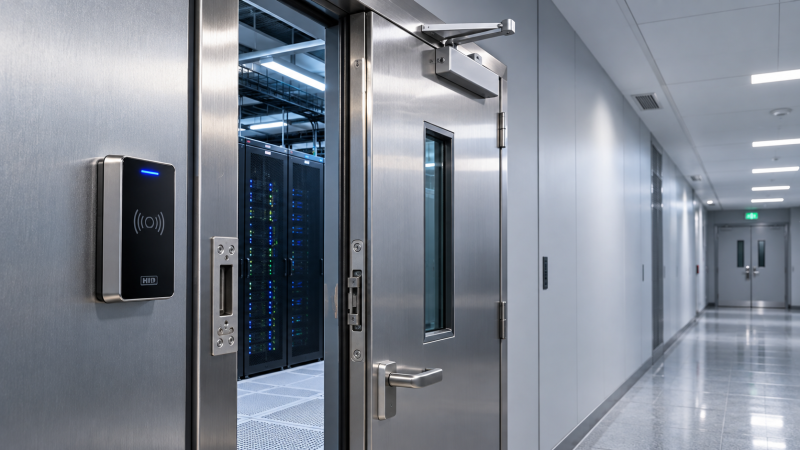
Assess the complete opening, including the door, frame, locking hardware, position sensor, reader, controller, and wiring. Strong electronics cannot compensate for an easily bypassed physical assembly.
Where UL 294 applies, verify the actual listing and installation conditions. A listed component does not establish that every assembled configuration or building installation is compliant.
Keep a traceability matrix linking each applicable requirement to design evidence, a test procedure, and an acceptance result. This makes unresolved weaknesses visible before handover.
How should cybersecurity standards influence system selection?
Modern access control platforms contain networked controllers, management servers, mobile applications, and cloud services. Their cybersecurity must be evaluated alongside locks, readers, and physical barriers.
ISO/IEC 27001 establishes information security management system requirements. Certification can support supplier assurance, but its value depends on whether the relevant services fall within scope.
ISO/IEC 27002 provides control guidance covering subjects such as access management, logging, cryptography, and supplier relationships. Use these controls to formulate concrete questions about implementation.
For example, require individual administrator accounts, appropriate multifactor authentication, role separation, and recorded configuration changes. Verify that privileged access can be revoked promptly across relevant services.
Examine network segmentation, exposed interfaces, certificate management, update authenticity, and vulnerability handling. Ask suppliers to demonstrate their processes using documented examples and supported product configurations.
IEC 62443 may provide additional guidance where access control connects with industrial automation or operational technology. Select relevant parts according to the architecture and responsibility boundaries.
Avoid accepting an unspecified claim of IEC 62443 compliance. Organizational processes, system security requirements, and component requirements involve different evidence and cannot be treated as interchangeable assurances.
Do credentials and reader connections resist realistic attacks?
Credential evaluation should examine cloning resistance, authentication methods, key management, revocation, and lost credential handling. Card appearance or a familiar technology name establishes little security assurance.
Map the complete authentication path from credential to reader, controller, and management platform. Identify where secrets exist, who controls them, and how compromised keys are replaced.
Legacy Wiegand connections generally lack native encryption and mutual authentication. Where interception or manipulation is credible, assess migration to an authenticated, encrypted reader communication approach.
OSDP, standardized through IEC 60839-11-5, supports interoperable reader communication and a secure channel capability. Confirm that secure channel protection is actually enabled and properly commissioned.
Protocol support alone does not establish secure operation. Check key provisioning, installation mode handling, device replacement, downgrade exposure, and the system’s response to communication tampering.
For mobile credentials, examine device binding, enrollment assurance, offline behavior, and revocation timing. Test what happens when an employee loses a phone or changes employment status.
Biometric deployments require additional scrutiny of presentation attack detection, template protection, and recognition performance. Relevant ISO/IEC 30107 and ISO/IEC 19795 provisions can inform those assessments.
Which local requirements can override a security preference?
Access control must preserve required escape routes and emergency operation. Applicable building and fire rules can determine locking arrangements, release mechanisms, signage, and inspection requirements.
In United States projects, adopted building codes, NFPA 101, and NFPA 70 may be relevant. Applicability depends on local adoption, occupancy, installation type, and enforcement.
Other jurisdictions use different regulatory frameworks and adopted standards. Identify the authority having jurisdiction early, particularly when controlled doors serve occupied spaces or designated escape routes.
Evaluate fail safe and fail secure behavior for each opening. The correct arrangement depends on egress hardware, fire requirements, security objectives, and the approved design.
Test power loss, fire alarm interfaces, emergency release controls, and restoration behavior. Confirm that required egress remains available under the conditions specified by applicable rules.
Privacy obligations also affect access logs and biometrics. Define lawful processing, retention periods, access permissions, and deletion procedures according to the jurisdictions governing the deployment.
Accessibility requirements deserve explicit review, including reader placement, usable controls, and door operation. Security improvements should preserve the facility’s required accessibility features and accessible routes.
How do you turn standards into measurable acceptance tests?
Write acceptance criteria before comparing proposals. Each criterion should identify the threat or operational need, expected behavior, test conditions, evidence owner, and pass or fail threshold.
For credential revocation, define the maximum acceptable propagation time across connected and temporarily disconnected controllers. Measure actual results under the network conditions expected at the facility.
For door monitoring, test forced opening and prolonged opening events. Verify alarm delivery, event timestamps, operator acknowledgment, and escalation against the approved operational response procedure.
For resilience, interrupt controller communications and management server availability separately. Confirm which decisions remain local, which events are buffered, and how records reconcile after recovery.
For backup power, calculate required autonomy from applicable requirements and site risk. Validate performance using the installed load and documented assumptions about battery condition and temperature.
For integrations, verify that identity changes, alarm events, and video associations remain accurate across systems. Include duplicate identities, time synchronization errors, and unavailable downstream services.
Set thresholds according to facility needs instead of borrowing universal numbers. A public lobby, research laboratory, and critical infrastructure control room require different acceptance criteria.
Record failures with reproducible steps, operational consequences, and remediation owners. Retest corrective actions before acceptance, especially where defects affect emergency behavior or unauthorized access prevention.
What evidence separates credible compliance from a marketing claim?
A useful supplier evidence package identifies the assessed product, applicable standard edition, test scope, issuing organization, and configuration limitations. Verify significant claims with the issuer where possible.
Distinguish certification, laboratory testing, and supplier declarations. Each provides a different level and scope of assurance; procurement documentation should state which evidence each requirement needs.
Request architecture diagrams, supported version lists, hardening guidance, update policies, and end of support dates. These documents reveal whether protection can be sustained throughout the intended lifecycle.
Ask who owns credential keys, configuration exports, event data, and integration documentation. Restricted access to these assets can increase migration costs and complicate incident recovery.
Evaluate maintenance responsibilities across the manufacturer, integrator, cloud provider, and facility operator. Unassigned responsibilities often create gaps in patching, monitoring, backup testing, and credential administration.
For high risk requirements, make documentary review a prerequisite and demonstration a separate acceptance condition. Evidence should support both product capability and the installed system’s behavior.
Which improvements should evaluators prioritize first?
Prioritize findings by consequence, exposure, exploitability, and remediation effort. Address unsafe egress, readily bypassed openings, compromised credentials, and exposed administrative access before optimizing convenience features.
Then examine dependencies that multiply risk across doors or buildings, including shared keys, central identity services, network access, and unsupported controllers with no viable update path.
Compare lifecycle costs alongside purchase price. Include commissioning, licensing, credential replacement, maintenance, vulnerability remediation, staff training, and eventual migration when assessing the value of alternatives.
The strongest security optimization standards strategy produces a clear evidence chain: applicable requirements, verified design choices, tested installation behavior, and assigned operational responsibilities throughout the lifecycle.
For technical evaluators, the final decision should identify what the system demonstrably protects, under which conditions, and which residual risks the facility must manage over time.